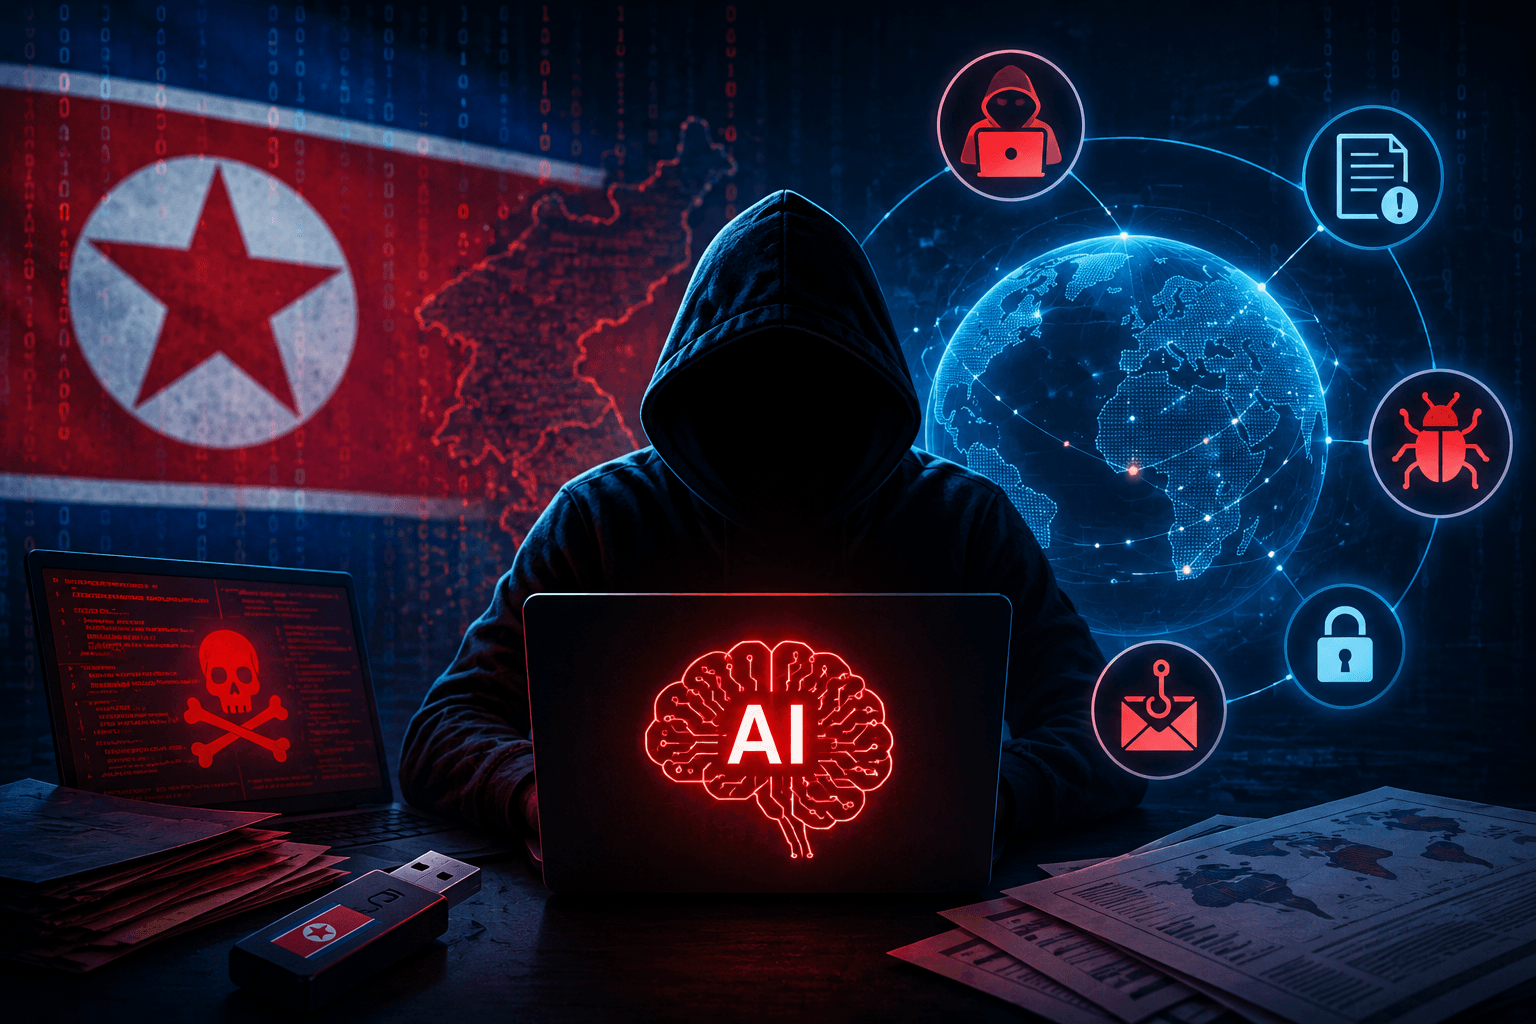
North Korea’s hacking operations are entering a new phase: artificial intelligence is no longer being used only to write better phishing messages. A new report suggests the Kimsuky cyber-espionage group is building an AI Arsenal capable of supporting document analysis, malware development and broader attack automation.
South Korean cybersecurity firm Genians said it found evidence that Kimsuky had deployed local large language model (LLM) tools including Ollama, GPT4All and Msty, together with retrieval-augmented generation (RAG) technology. The discovery is significant because locally operated AI can process sensitive material without sending it to an external AI provider.
From AI-assisted phishing to AI-enabled operations
Generative AI has already lowered the effort required to produce convincing emails, translations and fake documents. Kimsuky appears to be moving beyond that model.
According to Genians, the infrastructure also included AI-agent development frameworks, speech-to-text software and Cursor, an AI-assisted coding platform. Researchers believe these tools could help attackers analyze stolen information, develop software and make cyber operations more scalable.
The firm also identified finance- and cryptocurrency-themed documents that appeared to have been generated with AI. Such realistic material could make social-engineering campaigns harder for victims to distinguish from legitimate business communications. The findings, however, have not been independently verified.
Why local AI matters
The use of locally hosted models is particularly important. Public AI services can introduce restrictions, monitoring and data-leakage concerns. Running models on controlled infrastructure potentially gives an attacker greater privacy and flexibility.
RAG adds another capability: instead of relying only on what a model learned during training, it can retrieve information from a collection of documents and use that material while generating responses. In a malicious setting, that could potentially help organize and search large quantities of stolen information.
This does not mean Kimsuky has created an autonomous super-hacker. Rather, AI can reduce repetitive human work and allow relatively small teams to process more information and produce more convincing content.
A wider AI-cybersecurity trend
The development comes amid growing evidence that state-linked hackers are experimenting with AI. In May, Google reported that North Korean and Chinese threat groups had shown interest in using AI to identify cybersecurity weaknesses.
Kimsuky has also previously been linked to AI-assisted malware development. A May 2026 report described signs that an LLM had helped generate parts of the code associated with the HelloDoor malware.
The broader threat is therefore not simply AI-generated phishing. It is the gradual integration of AI into multiple stages of cyber operations.
For defenders, that means traditional security awareness alone may no longer be enough. Organizations will increasingly need stronger identity controls, endpoint monitoring, data protection and systems capable of detecting unusual behavior.
The emerging lesson is straightforward: AI is becoming a force multiplier for both attackers and defenders—and the cybersecurity race is accelerating.